A key that reaches a model ends up in the provider's logs. The app keeps them back in several layers, and each layer has an edge worth knowing.
Credential reads are refused
The app's own file tools refuse a credential store in every mode: "Refused: … is a credential store, and no seat may read one." A .env file, private key or keystore outside the workspace is refused by name. Both are recorded in the audit log. The same stores are denied to commands by the sandbox, and a command that names one asks even in Auto.
Keys are masked on the way out
Before a turn or a tool result leaves the Mac, anything shaped like an Anthropic, OpenAI, GitHub, xAI, Google, AWS, Slack or Stripe key, a JWT, a private-key block, or the password in a database URL becomes a placeholder such as [key-1]. The same key keeps the same placeholder for the run, so a model can still reason about it. A placeholder is never turned back into the key, and the run ends with a notice saying how many were masked. There is no switch.
The limit: this covers what the app itself sends. A command-line seat reads files with its own tools and talks to its own provider directly, so the mask does not see that traffic. Keep keys out of the workspace, or use a deny read rule, if a CLI seat works there.
Variables are scrubbed
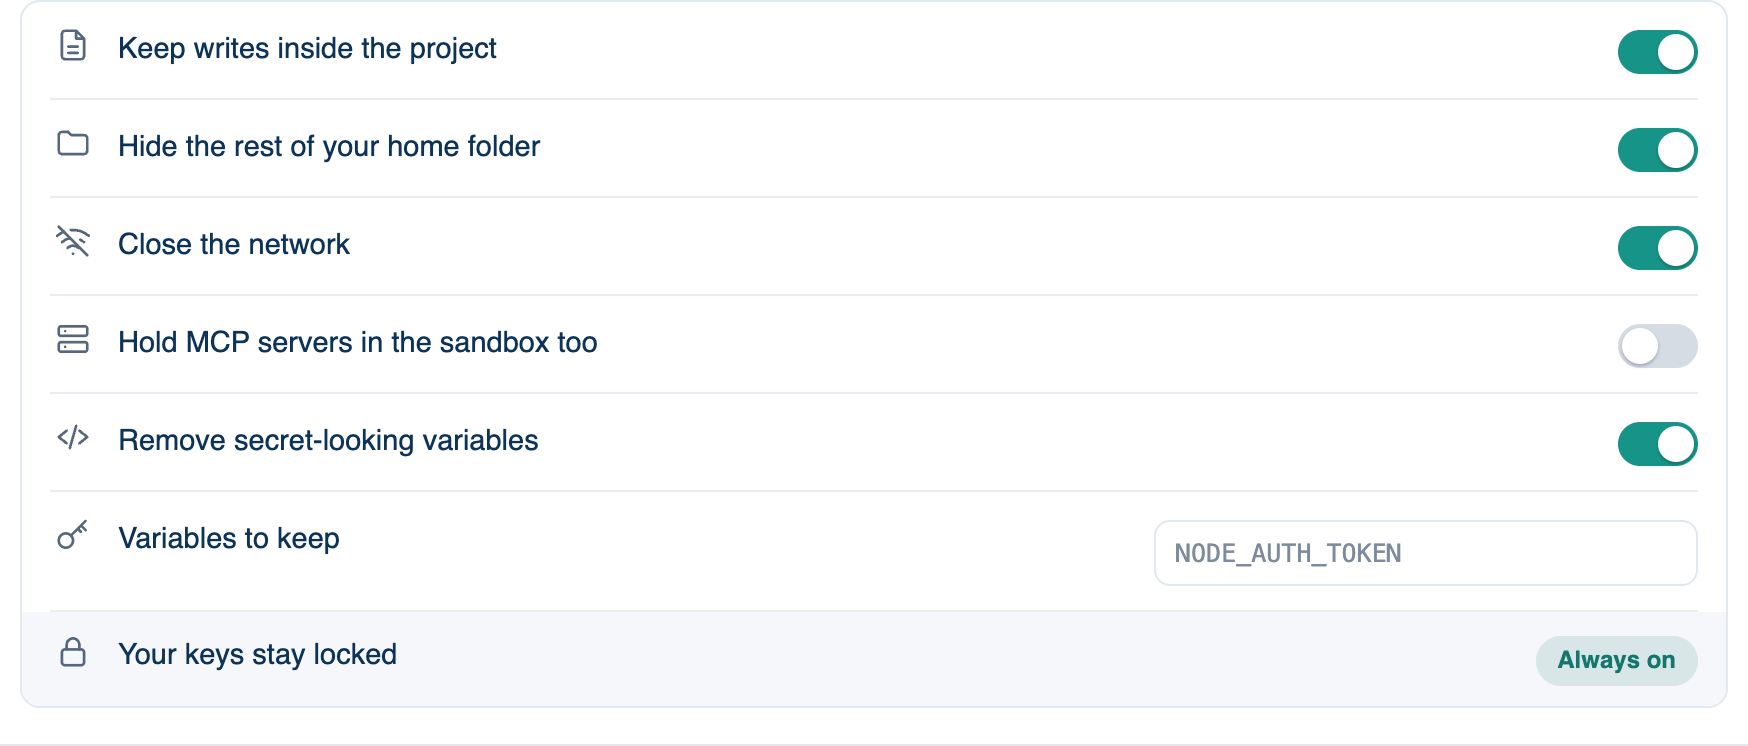
With Remove secret-looking variables on (the default), token-shaped environment variables are taken out before a command or seat starts. A team can name more, and team secrets are passed in by name with their values masked from every transcript.
Personal data (teams)
A team owner can switch on redaction of emails, phone numbers, card numbers and social security numbers in what the room fetches on the Mac. On the server, personal data can be masked before a prompt leaves and put back in the answer. Both are in Governance. A path matched by a classify read rule reaches a seat as a handle with its size and shape, not its content, and the seat can place it into a file without the data entering a model.
When you push
The ship check looks at added lines for keys, at dependency advisories, and at access checks that went the wrong way, when you push or open a pull request. It is shown, not enforced, unless your team makes it a gate. A diff of a secret file stays on the machine running the discussion and is not mirrored to your other devices.
Further reading. LLM01:2025 Prompt Injection — OWASP, 2025. OWASP Top 10 for LLM Applications 2025 — OWASP.